
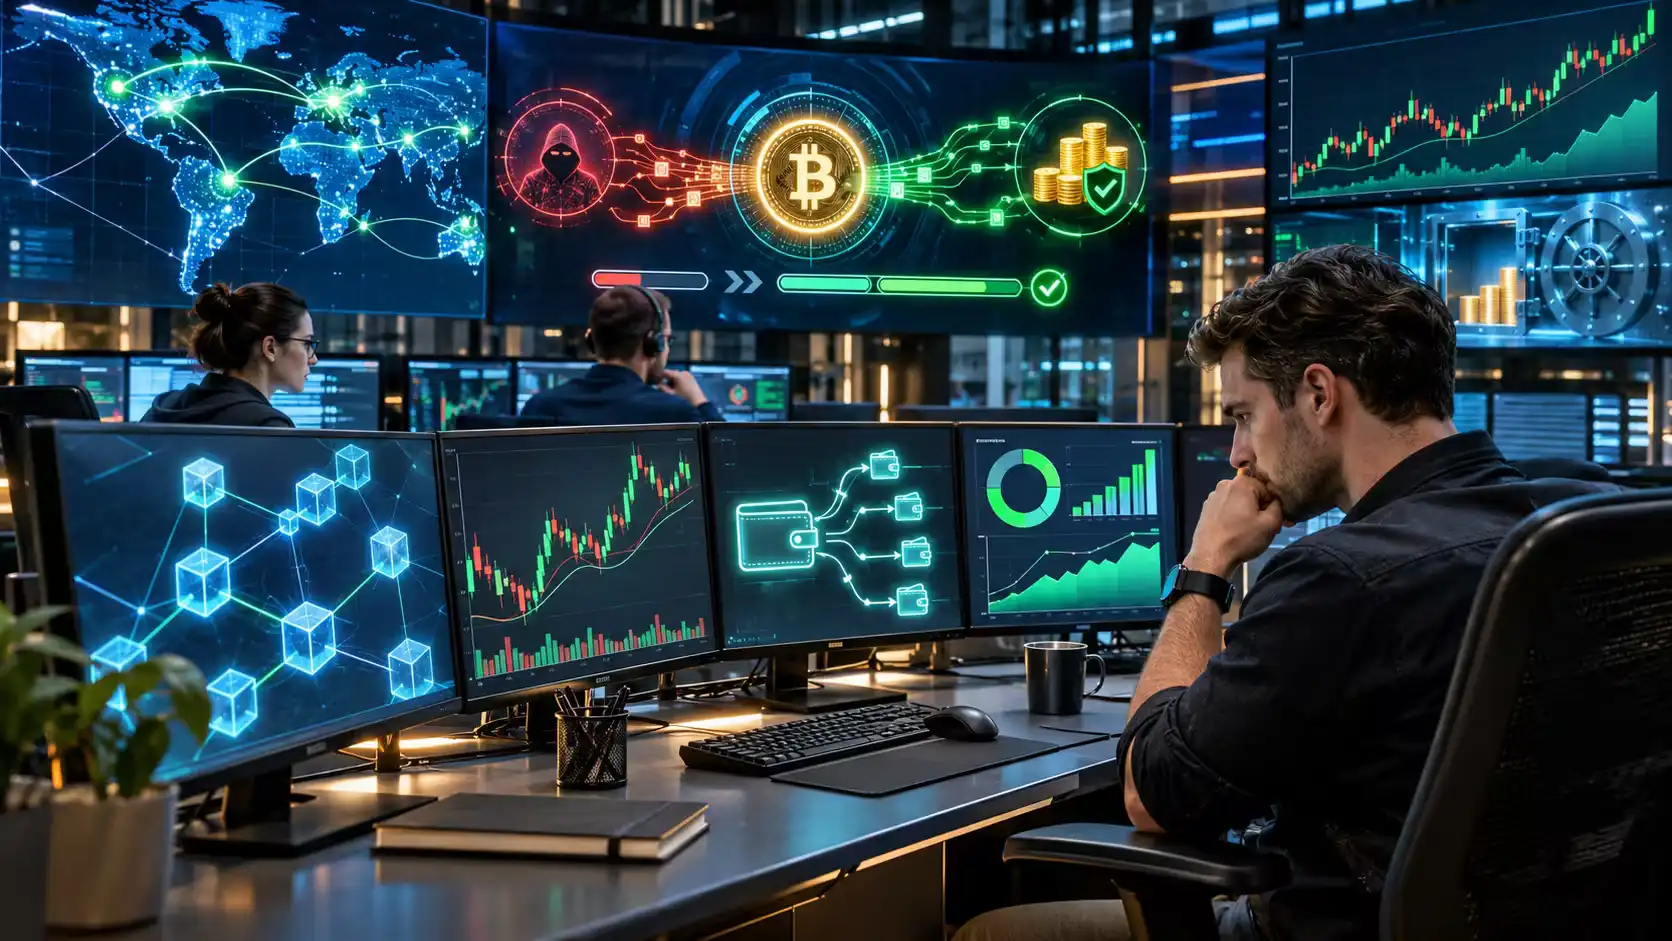
Binance is rebuilding its cryptocurrency reserves and gradually restoring withdrawal services following a record-breaking $6.34 billion crypto heist on 29 October 2026.
The attack, which US investigators have attributed to North Korea-linked hackers, has become one of the most significant security incidents in cryptocurrency history.
By 4 November, Binance confirmed it had replenished approximately 98% of the affected digital assets, using its own financial resources and emergency protection funds.
Meanwhile, investigators and industry partners had frozen or intercepted approximately $2.85 billion in stolen cryptocurrency.
These figures represent two different aspects of the recovery. Replenishing customer assets does not mean the exchange has recovered the same amount directly from the hackers.
The incident has also tested confidence in centralised cryptocurrency exchanges. Customers withdrew billions of dollars after Binance restarted withdrawals, while Bitcoin, Ethereum and BNB experienced substantial selling pressure following news of the attack.
What Is the Latest Update on the Binance $6bn Crypto Heist Recovery?
Binance’s latest recovery announcement on 4 November confirmed that approximately 98% of the affected token assets had been replenished, leaving around 2% outstanding.
The company explained that the remaining assets were relatively illiquid cryptocurrencies, making them more difficult to purchase in the necessary quantities.
By 5 November, Binance had announced another phase of withdrawal restoration, with additional assets scheduled to become available from 04:00 UTC, subject to security checks.
Binance Crypto Hack Recovery
| Recovery indicator | Latest reported position |
| Date of attack | 29 October 2026 |
| Estimated crypto stolen | $6.34 billion |
| Assets frozen or intercepted | Approximately $2.85 billion |
| Estimated proportion frozen | Around 45% |
| Affected assets replenished | 98% |
| Outstanding replenishment | Around 2% |
| Funds allocated to cover losses | More than $6.34 billion |
| Net customer withdrawals by 2 November | $4.72 billion |
| Main suspected perpetrators | North Korea-linked TraderTraitor |
| Withdrawal services | Reopening progressively |
| Latest reserve snapshot | 44 tokens covered |
The most important development is Binance’s commitment to absorbing the losses instead of passing them on to customers.
In its official recovery announcement, the company confirmed that it had allocated more than 100% of the funds required to cover the incident.
However, the investigation and recovery of the actual stolen cryptocurrency remain ongoing.
How Did Hackers Steal $6.34 Billion From Binance?
The Binance hack was not simply a case of criminals guessing passwords or breaking Bitcoin’s underlying cryptography.
According to Binance’s preliminary investigation published on 3 November, attackers used a coordinated campaign involving malicious software, fake recruitment interviews, compromised employee computers and unauthorised access to the exchange’s internal wallet-signing infrastructure.
The Attack Began Months Before the Theft
Binance identified several important stages in the intrusion:
- June 2026: A wallet infrastructure engineer downloaded a compromised software installation while attempting to install an AI development tool. Although Binance detected that incident and replaced the affected device, information about the engineer’s role and colleagues was exposed.
- September 2026: Another engineer was approached by someone pretending to represent a legitimate employment opportunity. A fake interview process persuaded the employee to download a malicious coding assignment.
- 20 October 2026: Attackers used the compromised computer and an internal AI tool to extend their access into Binance’s wallet development environment.
- 29 October 2026: The attackers used compromised systems and credentials to initiate unauthorised cryptocurrency transfers.
The actual theft began at approximately 20:05 UTC on 29 October.
Within minutes, large amounts of XRP and other digital assets were transferred to attacker-controlled wallets. The attack subsequently affected multiple blockchain networks, including Bitcoin, Ethereum, Solana and Optimism.
One especially significant weakness involved Ethereum’s EIP-7702 authorisation mechanism.
The attackers exploited access to Binance’s signing infrastructure to create malicious wallet authorisations. Some of those permissions remained active independently of Binance’s normal withdrawal processes, complicating the exchange’s attempts to stop the theft.
Why this matters: The incident demonstrates that even when blockchain cryptography remains intact, the infrastructure used to manage cryptocurrency can still be compromised.
Who Was Responsible for the Binance $6bn Crypto Heist?
The FBI attributed the attack to TraderTraitor, a North Korean state-linked cybercrime group associated with a broader network of cryptocurrency-focused hacking operations.
In its official statement published on 31 October 2026, the FBI identified North Korea as responsible for the theft.
The agency also reported that the attackers were converting stolen assets into Ether and could use decentralised finance platforms and instant-exchange services to conceal their movements.
North Korea has denied the allegations.
Blockchain analytics companies independently identified transaction patterns connecting the Binance theft with previously investigated North Korea-linked cryptocurrency attacks.
Dr Tom Robinson, founder and chief scientist of blockchain intelligence company Elliptic, published an independent analysis identifying approximately $6.43 billion in stolen cryptocurrency across 11 blockchains.
His research showed that the attackers used Binance’s own signing infrastructure to authorise malicious transactions. The findings highlight the importance of protecting employees, internal systems and wallet approval processes, rather than relying solely on the security of the blockchain itself.
Elliptic also identified extensive movement of stolen funds between blockchain networks, complicating efforts to prevent further laundering.
How Much of the Binance Stolen Cryptocurrency Has Actually Been Recovered?
The distinction between stolen funds being frozen, assets being replenished and money being recovered is essential to understanding the Binance recovery.
By 3 November, Binance reported approximately $2.85 billion in stolen digital assets had been frozen or intercepted.
That represents roughly 45% of its estimated $6.34 billion loss.
However, frozen assets are not necessarily assets that Binance has already regained control of.
Frozen Funds Versus Replenished Funds
| Category | Meaning | Reported amount |
| Stolen cryptocurrency | Assets transferred out by the attackers | $6.34bn |
| Frozen or intercepted assets | Stolen funds blocked or secured through intervention | $2.85bn |
| Replenished customer assets | Assets Binance has replaced from available resources | Approximately 98% |
| Remaining replenishment | Illiquid assets still being acquired | Approximately 2% |
Stablecoin issuers played an important role in containing the damage.
Companies including Tether and Circle have mechanisms that can freeze certain tokens associated with illicit transactions. Investigators worked with these organisations and other industry partners to restrict access to stolen funds.
Nevertheless, native cryptocurrencies such as Bitcoin and Ether generally cannot be frozen by a central token issuer.
This difference explains why the speed of intervention was so important.
Some stolen assets could be blocked before the attackers converted them, while others were moved into cryptocurrencies that are more difficult to restrict.
Even if Binance completes the remaining 2% of its reserve replenishment, that will not automatically mean every stolen asset has been returned.
How Is Binance Paying for the $6bn Crypto Hack?
Binance has committed to covering the financial impact of the attack using its Secure Asset Fund for Users (SAFU), other company resources and relevant insurance reserves.
The SAFU fund was established in 2018 to help protect customers against exceptional incidents, including certain exchange security breaches.
Following the October attack, Binance said that its own resources would be sufficient to replace the affected assets.
Its initial recovery programme involved holding billions of dollars in the same cryptocurrencies that had been stolen, while buying additional tokens through exchanges and over-the-counter trading arrangements.
Where the Replacement Funds Are Coming From?
Binance has identified three principal sources of funding:
- Secure Asset Fund for Users: Emergency reserves intended to help protect customers during extraordinary events.
- Futures insurance reserves: A portion of the exchange’s existing insurance resources, subject to applicable requirements.
- Corporate treasury: Binance’s own financial resources, used to acquire and replace the affected assets.
Binance has also committed to rebuilding the SAFU fund to approximately $1 billion.
The remaining challenge involves purchasing cryptocurrencies that have relatively limited market liquidity.
Buying large quantities of smaller tokens can be difficult without significantly affecting their market prices.
This is why Binance’s asset replacement programme has progressed more quickly for major cryptocurrencies than for some less-liquid tokens.
Are Binance Customers Getting Their Money Back?
Binance maintains that customers will not bear the direct financial impact of the stolen assets.
However, account balance protection and withdrawal accessibility are separate matters.
After identifying the breach, Binance temporarily suspended withdrawals while investigating the affected infrastructure and strengthening its security controls.
Withdrawal services began reopening on 1 November, initially covering selected major cryptocurrency networks.
The exchange subsequently extended access to additional assets.
On 5 November, Binance announced another expansion covering selected tokens across Ethereum, BNB Smart Chain, Base, Tron, Polygon and Sui networks.
The company also warned that not every asset would become available simultaneously.
Customers attempting to withdraw funds may therefore encounter temporary restrictions or processing delays, depending on the cryptocurrency and blockchain network selected.
Binance co-chief executive Richard Teng acknowledged the seriousness of the incident during Hong Kong Fintech Week on 3 November.
“It’s a painful lesson. We take responsibility for it,” Teng said.
He also maintained that Binance remained in “very strong financial health”, arguing that the exchange had sufficient resources to cover the losses.
These statements provide reassurance about the company’s intended response, but the recovery remains dependent on completing asset replenishment, restoring normal services and establishing confidence in the upgraded security systems.
Why Did Investors Withdraw Billions From Binance After the Hack?
One of the most immediate consequences of the attack was a sharp increase in customer withdrawals.
On 1 November, Binance had processed approximately $4.6 billion in withdrawals alongside $1 billion in deposits, resulting in net outflows of about $3.6 billion.
By 2 November, cumulative net withdrawals had increased to approximately $4.72 billion, equivalent to around 3% of the assets held on the platform at that point.
The figures indicate that some customers wanted to reduce their exposure to the exchange while investigations continued.
However, they do not establish that Binance was experiencing a sustained liquidity crisis.
Richard Teng subsequently reported that hourly inflows and outflows had largely returned to normal.
From a financial risk perspective, the withdrawal activity is significant because it measures how customers respond when an exchange experiences a major operational failure.
The incident also demonstrates why investors should consider security, custody arrangements and liquidity alongside the charges examined in a crypto exchange fees comparison.
Low trading fees provide little benefit if users cannot access their assets when necessary.
What Happened to Bitcoin, Ethereum and BNB After the Binance Hack?
The Binance security breach contributed to a period of selling pressure across major cryptocurrency markets.
Following the disclosure, Bitcoin fell by nearly 5%, Ethereum declined by almost 6%, and BNB experienced a decline approaching 10%, according to contemporary market reporting.
These movements occurred amid broader market volatility, so the entire decline cannot necessarily be attributed to the hack alone.
Nevertheless, the incident created several clear sources of uncertainty.
First, investors questioned whether further unauthorised transfers could occur.
Second, the temporary withdrawal suspension raised concerns about access to funds.
Third, the substantial value of stolen cryptocurrency prompted speculation about whether the attackers would liquidate assets through exchanges or decentralised trading platforms.
Blockchain investigators subsequently identified efforts to convert stolen stablecoins into Ether and other assets.
Such activity can complicate recovery and create transaction-level disruption across decentralised markets.
The longer-term market impact will depend partly on whether the remaining stolen funds are contained and whether Binance can demonstrate that its wallet infrastructure has been secured.
How Does the Binance Hack Compare With Previous Crypto Heists?
The scale of the Binance incident is extraordinary even by the standards of previous cryptocurrency attacks.
According to Elliptic’s analysis, the estimated $6.43 billion stolen on 29 October was more than four times the amount lost during the major Bybit breach in February 2025.
| Incident | Date | Estimated crypto stolen |
| Binance hack | October 2026 | $6.34bn–$6.43bn |
| Bybit hack | February 2025 | $1.46bn |
The figures use estimates reported by the affected exchanges and blockchain investigators and are not adjusted for subsequent cryptocurrency price movements.
The two incidents also share an important security concern.
In both cases, investigators identified vulnerabilities involving systems or individuals responsible for managing cryptocurrency wallet transactions.
This raises questions about how major exchanges separate operational access from authorisation to move customer assets.
What Does the Binance $6bn Crypto Heist Mean for UK Investors?
For UK investors, the Binance incident highlights the risks associated with keeping substantial cryptocurrency holdings on centralised trading platforms.
When cryptocurrency is stored through an exchange, customers typically rely on the platform to maintain custody arrangements, secure private keys and authorise transfers correctly.
A compromise of those systems can create problems even if the underlying blockchain has not been hacked.
Exchange Security Is Different From Wallet Ownership
Investors holding cryptocurrency directly in a non-custodial wallet control their own private keys.
This removes dependence on an exchange’s custody infrastructure, although it introduces different risks, including lost recovery phrases, phishing scams and malicious transactions.
Investors considering this approach can review the practical requirements of creating a Bitcoin wallet, including secure recovery phrase storage.
The same considerations apply to investment platforms offering cryptocurrency staking services.
Before transferring assets, investors should assess the custody model, withdrawal restrictions and counterparty risks associated with the best crypto staking platforms.
Importantly, Binance’s promise to reimburse customers is a company commitment, not evidence of an industry-wide financial guarantee.
The UK’s Financial Conduct Authority has warned that investors in most cryptoassets should not expect protection from the Financial Services Compensation Scheme if something goes wrong.
A broader UK cryptoasset regulatory regime is scheduled to begin on 25 October 2027, but investors should not assume that future authorisation will make every cryptocurrency investment eligible for compensation.
For customers affected by the Binance incident, the practical priorities are checking official service updates, monitoring withdrawal availability and avoiding unsolicited recovery offers.
Scammers may attempt to exploit uncertainty by impersonating exchange support staff or offering to recover stolen cryptocurrency in return for upfront payments.
What Happens Next in the Binance Crypto Heist Investigation?
Although Binance has made substantial progress replacing affected assets, several important questions remain unresolved.
The first concerns the final recovery of the stolen cryptocurrency.
With approximately $2.85 billion frozen or intercepted in the early stages, investigators continue to face the challenge of tracing assets that have been converted or transferred across multiple blockchains.
The second concerns technical security.
Binance says it has rebuilt affected wallet infrastructure, replaced compromised devices, revoked relevant credentials and introduced additional monitoring controls.
It has also committed to an independent cybersecurity review.
A complete assessment of the incident will need to establish whether the revised controls address the weaknesses that allowed attackers to access sensitive wallet-signing systems.
The third concerns transparency.
On 4 November, Binance published an updated Proof of Reserves snapshot covering 44 cryptocurrencies, compared with ten in the preceding snapshot.
The company indicated that generating the associated zero-knowledge verification proof would require approximately 50 to 60 hours.
Once available, that proof should allow eligible customers to check the backing of their reported balances.
Proof of Reserves provides useful evidence about asset holdings, although it should not automatically be treated as a complete independent audit of every financial obligation or operational risk.
For Binance, the strongest evidence of recovery will be the completion of asset replenishment, the restoration of ordinary withdrawal access and the publication of independently reviewed security findings.
Conclusion
The Binance $6bn crypto heist recovery has progressed rapidly, with the exchange reporting that 98% of affected cryptocurrency assets had been replenished by 4 November 2026.
However, replacing stolen customer assets is not the same as recovering funds from the attackers. Approximately $2.85 billion had been frozen or intercepted, while investigations into the remaining stolen cryptocurrency continued.
Binance’s financial commitment has helped limit immediate customer losses, but the attack has exposed serious vulnerabilities in cryptocurrency custody infrastructure. Its long-term recovery will depend on restored withdrawals, stronger security controls, independent verification and the ability to rebuild investor confidence.
Frequently Asked Questions
Has Binance Recovered All $6 Billion Stolen in the Hack?
No. Binance reported replenishing 98% of affected assets by 4 November, but that does not mean 98% of the stolen funds were recovered from hackers. Approximately $2.85 billion had been frozen or intercepted.
Who Hacked Binance in October 2026?
The FBI attributed the attack to TraderTraitor, a North Korea-linked hacking group. North Korea has rejected the accusation, while blockchain investigators have identified evidence consistent with the FBI’s attribution.
Will Binance Refund Customers Affected by the Hack?
Binance has committed to absorbing the full financial impact using its own resources and protection reserves. The company says customers will not bear the direct losses caused by the theft.
Can Customers Withdraw Cryptocurrency From Binance Now?
Binance has been reopening withdrawals in phases since 1 November 2026. Availability depends on the cryptocurrency and network, and users should check the current status before initiating a withdrawal.
How Much Cryptocurrency Was Frozen After the Binance Heist?
Binance reported approximately $2.85 billion in stolen cryptocurrency had been frozen or intercepted. This represents around 45% of the exchange’s estimated $6.34 billion loss.
Was Bitcoin Itself Hacked During the Binance Attack?
No evidence indicates that Bitcoin’s underlying blockchain cryptography was compromised. The attack targeted Binance’s internal systems and wallet-signing infrastructure, allowing unauthorised cryptocurrency transfers.
Is Binance Safe to Use After the $6bn Hack?
Binance has introduced additional security controls and committed to an independent investigation. However, the effectiveness of those changes cannot be conclusively assessed until further independent findings and full service restoration are available.